How to Manage Shadow IT: A Step-by-Step Guide for IT and Security Leaders

To manage shadow IT, start by creating visibility into the tools people use, then talk to the teams using them to understand why. Set priorities by risk, decide which tools to approve, replace or retire, and give employees governed tools that are as easy to use as the apps they chose themselves. Messaging and crisis communication need a plan of their own. Shadow IT is rarely a sign of bad intent.
Secure Document Sharing Platform: Features to Look For & Best Tools

Enterprises share confidential documents every day, from financial reports and legal contracts to government records, customer information, and internal strategy documents. These files frequently move between departments, external partners, contractors, and clients, often through several tools before the work is complete. A secure document sharing platform lets your team share these confidential files while maintaining security and compliance.

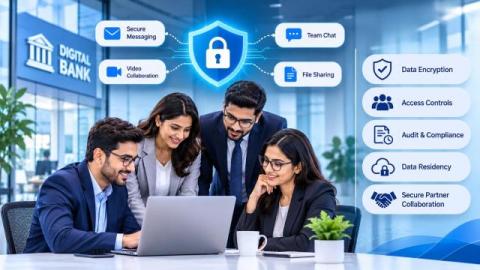
How Secure Team Communication Supports Digital Banking Operations

A payment batch fails at 2 a.m. Within minutes, engineers and compliance staff are trading messages about which customers are affected. Whatever tool carries that conversation also carries customer data and the decisions a regulator may ask about later. For a digital bank, team communication is part of the operating infrastructure.

PSA security and compliance: what finance leaders should check before signing

PSA security and compliance means checking two things: that a vendor's controls are independently proven, and that your permissions keep margin data with the right people. PSA here means a professional services automation platform, which connects projects, resources and financials, not the IoT security scheme that shares the acronym. At Teamwork.com I brief agencies and research partners from the client side, and I'll take one dated, readable report over a wall of badges.

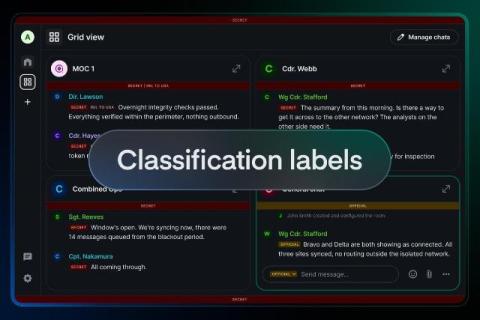
Implementing security labels in Matrix

A talk by Midhun Suresh R and Kieran Lane at The Matrix Conference 2026. Defence and government organisations need to share classified information quickly, with their own people and with allies, without it ever reaching someone who isn't cleared to see it. Speaking at The Matrix Conference, Midhun Suresh R. and Kieran Lane showed how the Mission Partner Environment (MPE) add-on for Element Server Suite Pro (ESS Pro) makes that possible.

Data Breach Detection In BFSI For Audit And Regulatory Readiness In 2027

in 2026, financial regulators around the world judge a breach by how quickly you detected it and what evidence you can show, not by the controls you bought. The key points: Most banks and insurers don’t lose the regulatory argument because a breach happened. They lose it in the hours that follow, when an auditor asks a simple question: when did you first know? If the honest answer is “when a customer complained,” no policy document will save the review.

Zero Trust Security: Principles, Benefits & Implementation

Zero trust security is a cybersecurity approach that requires organizations to verify users, devices, and applications before granting access to sensitive resources. As enterprises adopt cloud services, support remote employees, and collaborate with other departments and external partners, security teams have to manage more identities, devices, and access points. Zero trust helps with that.

A CIO And CISO Guide To Preventing Enterprise Data Leakage Under DPDP

Ten years ago, sensitive data left an enterprise through email attachments, file shares and the occasional USB drive. Today most of it leaves through a browser tab. Customer records live in SaaS CRMs, ticketing tools and banking portals, and the routes out of those apps are a paste into a personal chat window, an upload to personal storage, a screenshot or a prompt typed into a public AI assistant.