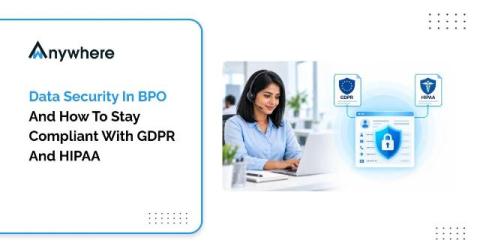
Data Security In BPO And How To Stay Compliant With GDPR And HIPAA
BPOs meet GDPR and HIPAA by combining contract obligations with controls on every seat, namely verified identity, restricted access, protection against data leaving the device, and complete activity logs. Many of these controls satisfy both frameworks at once, which makes one well-designed security program far easier to run than two separate ones.